Stop being a victim of Ransomware and take action today!
PYSA Ransomware is a unique threat, stemming from the Mespinoza Ransomware family. Many enterprises and educational institutions have been victimized by it in the last year and a half, leading to some very harsh outcomes.
PYSA Ransomware Data Recovery Services
To prevent your enterprise from being further damaged by PYSA, you need the help of seasoned ransomware experts. Alvaka is an experienced ransomware recovery and security company that can help you. Our expert team can detect PYSA ransomware on your system, remove it quickly, eject the hackers, and get you on the path to recovery. We’ll also protect systems from being attacked in the first place, preventing you from worrying about the pain of PYSA.
How Does PYSA Ransomware Work?
PYSA ransomware works like most ransomware threats. It finds its way onto your devices, where it will begin an encryption process. Essentially, the ransomware is encrypting your files and holding them ransom until you pay the demand. You’ll be unable to access your files unless you pay the hacker to lift the encryption.
It gets onto your system by phishing, meaning that you or some of your employees have been fooled by a seemingly innocuous email or download link, or through failure to apply software security patches each month.
What to Do If You’re Attacked by PYSA Ransomware
If you have been attacked by PYSA, you will notice that your files can’t be opened and they will have a new .pysa file extension. There will also be a README text file on your desktop that informs you of the encryption and that they will decrypt the files for a fee.
Here’s what to do in this situation:
Ignore everything in the text file and don’t follow any orders
Seek out expert help from a lawyer, also known as a breach coach.
Never ever negotiate with hackers in this scenario until you have gotten experienced help. There are also special OFAC regulations related to paying hackers, if that is what you feel is your only option. Violating these rules can make your situation worse. You are dealing with criminals, so there’s no guarantee they’ll stick to their word, or that they won’t leave some lingering software on your devices after decrypting. We can assist you in this area as well.
Why Choose Alvaka for PYSA Ransomware Recovery Services?
We offer PYSA ransomware removal and recovery services for your enterprise. As an experienced company, we have a team that’s fully equipped to scan your devices and decrypt your files as swiftly as possible. Alongside this, we can provide recovery services to remove the ransomware from your device and restore everything to how it used to be. We are also paneled by many of the insurance carriers. That means we are preauthorized to work on your ransomware recovery.
When you choose us, you get the following:
A swift and effective service that’s proven to work
Added protection against future threats
Education for employees in good cybersecurity habits
A qualified and experienced team that can handle any ransomware job
It’s crucial to act as quickly as possible whenever a PYSA ransomware attack happens. We’re here to assist you throughout the process of removal and recovery.
Contact us today at (949) 428-5001 to learn more about our services.
Alvaka PYSA Ransomware Recovery Services are designed to help companies recover from ransomware attacks and protect your systems from future attacks.
Stop being a victim of Ransomware and take action today!
HelloKitty ransomware is a file-locking Trojan that can find its way into your system undetected usually through phishing attacks or unpatched vulnerabilities.
What is HelloKitty Ransomware?
HelloKitty ransomware encrypts PC files and causes major issues for many businesses. Typically, this ransomware targets businesses, schools, and state and local governments of all types. It has been active since November 2020 and made the news after claiming to have stolen numerous games’ source codes from high-profile developers CD Projekt Red.
If you are the victim of a HelloKitty ransomware attack, you must get support right away.
How Does HelloKitty Ransomware Work?
In essence, it is a file-locking Trojan that finds its way onto your system undetected. Typically, this is via phishing attacks that deceive you or your employees, or through unpatched software on your network. Unpatched firewall vulnerabilities, such as the recent flaws in FortiGate’s, was cause for numerous outbreaks. Regardless of how it made it into your system, HelloKitty will then encrypt your files to prevent file content from opening. This creates a debilitating situation for anyone infected.
A ransom demand is then made by the hackers, stipulating that they will unlock your files once you have paid the ransom. It is crucial to seek guidance if you feel you need to pay. There are federal regulations related to the Treasury Department Office of Foreign Asset Control that can get you in trouble if you violate them. You can also never truly be sure that the hackers will keep their word, although we have not seen this to be a common issue.
What to Do If You’re the Victim of a HelloKitty Ransomware Attack?
HelloKitty ransomware attacks aren’t subtle, and they are easily identified by a text file appearing on your desktop. It will explain that your files have been encrypted, detailing more specifics, and telling you what to do to pay them.
If you have found this file on your system, here’s what you need to do:
Disconnect your devices from the Internet and other systems on the network right away
Avoid following any of the steps listed in the text file
Never engage with hackers or attempt to communicate with them, as they will try to take advantage of you. Instead, give us a call and let our expert team deal with things for you.
Why Choose Alvaka for HelloKitty Ransomware Recovery Services?
We’re an experienced ransomware recovery company that specializes in cybersecurity and ransomware attacks. We are paneled by many of the cyber breach insurance companies. That means we are authorized to do the recoveries for cyber breach-insured victims. We are also the first choice for many of the cyber breach coach lawyers that assist victim companies through the maze of issues related to a ransomware attack.
By choosing us, you benefit from the following:
Swift and effective HelloKitty ransomware recovery
A full scan of your system to help ensure no ransomware or Trojans exist
Detection services to find where the ransomware breached your system, along with solutions to tighten security and prevent it from happening again
Educational resources for employees to teach them how to detect phishing and prevent ransomware attacks
Put simply, you get a service that’s designed to remove HelloKitty ransomware and protect you from future attacks.
Contact us today at (949) 428-5001 if you’re the victim of an attack, or if you’d like protection from one!
Alvaka’s HelloKitty Ransomware Recovery Services are designed to help companies recover from ransomware attacks and protect your systems from future attacks.
Stop being a victim of Ransomware and take action today! BlackMatter ransomware is a newly emerging problem for enterprises across the board. It is a specific type of ransomware that can infiltrate your system, combining some of the tools and technologies of various other ransomware out there. The results can be devastating, and you’ll likely need the help of ransomware experts to recover from an attack.
BlackMatter Ransomware Data Recovery Services
At Alvaka, we’re a specialty security company with expertise in ransomware protection and removal. If you’re the victim of a BlackMatter attack, our team of experts can remove it from your system and put you back in control and operating again.
What is BlackMatter Ransomware and How Does It Work?
BlackMatter ransomware was first spotted in July 2020, and it is unique in that it brings together various features of some of the most potent and dangerous ransomware variants we’ve seen. In total, it combines features from the following:
DarkSide]
REvil
LockBit 2.0
BlackMatter will first infiltrate your system–typically via phishing or unpatched software–and then encrypt your files and replace the extensions with randomly generated numbers and letters. As a result, you’re unable to open any of your files until they have been decrypted.There are two massive problems with BlackMatter that make it so dangerous:
It’s fairly new to the scene, meaning not enough time has passed for there to be any free decryption tools for businesses to use. It is unlikely that a free decryption tool will be developed, but if so, it could take months to years to arrive.
It uses SHA-256 encryption, which is extremely high-level encryption that’s almost impossible for the average person to crack and decrypt.
Upon breaching your system, the attackers will demand some form of payment to decrypt your files for you. Currently, BlackMatter is targeting enterprise-level businesses that make a lot of money. Consequently, you need to ensure you’re protected from ransomware attacks, and that you can find a swift solution if your defenses are breached.
BlackMatter Ransomware Decryption Services
Thankfully, you’re in the right place for BlackMatter ransomware removal and recovery services. Alvaka is highly experienced in dealing with all types of ransomware. Our dedicated team of cybersecurity experts works around the clock identifying new forms of ransomware and developing ways of quickly recovering the systems. With our help, we can remove BlackMatter ransomware and help you recover your affected devices and get back to running your business.
What to Do If You’ve Been Affected by BlackMatter Ransomware
The first step is identifying if you have been attacked by this ransomware. As there are so many different variants around, it’s easy to think you’ve been attacked by one ransomware, when really another was at fault. This link is a free tool to help you identify which ransomware variant has infected you.Thankfully, it is relatively easy to spot BlackMatter ransomware on your system. Firstly, you will see a .txt file magically appear on your desktop, usually titled “README”. It will direct you to a dark web internet browser with information on how to speak to the hackers. Also, as mentioned before, a telltale sign of BlackMatter is seeing your file extensions changed to a series of random numbers and letters.If you have spotted these signs and believe you’ve been infected with this ransomware, be sure to do the following:
Disconnect the compromised systems from the network
Determine if you have cyber breach insurance
Don’t follow any instructions in the text file on your desktop
Call us immediately at (949) 428-5001! We are available 24×7×365.
Report the attack to the authorities
We also urge you to avoid all communications with the hackers. In our experience, negotiating with hackers is pointless, as they have all the control while you have nothing. Therefore, the only possible outcome is one that’s worse than the situation you’re already in.
Why Choose Alvaka as a BlackMatter Ransomware Removal Company?
Our company is built on outstanding expertise in the field of cybersecurity and ransomware. With a highly skilled team at our fingertips, we have all the knowledge and experience needed to help you deal with BlackMatter. We are approved for doing the ransomware recovery work by many cyber breach insurance companies and cyber breach coaches/law firms.When you choose Alvaka, you will enjoy the following:
Professional and swift recovery from BlackMatter ransomware
A system scan to identify how the ransomware got into your system, followed by security implementations to prevent it from happening again
Education for your employees to train them to avoid phishing scams and keep your business protected in the future
BlackMatter ransomware is no joke, and you can’t afford to let it stay on your network for any longer than necessary. Your business recovery is predicated on a successful ransomware recovery.If you’re the victim of a ransomware attack, contact us today at (949) 428-5001 for a fast and effective recovery!https://www.youtube.com/watch?v=AK8lfAzQmkgAlvaka’s BlackMatter Ransomware Recovery Services are designed to protect your company’s systems from Ransomware and recovery when necessary.
Click on each of the commonly asked questions below to see answers.
1. How do I recover from a ransomware attack?
Ransomware attacks are becoming increasingly common, and whether you are a small, medium, or large company, you are a target.
If you have been an unfortunate victim of a ransomware attack, you are likely overwhelmed and wondering what the next steps are. We have been involved in many recovery efforts and have outlined what our clients experience as the most common and important steps when recovering from a ransomware attack.
The process will be lengthy, expensive, and stressful but putting together a well-rounded recovery and response team will be invaluable. In the initial stages, engage a lawyer and find out what insurance covers. Have your response team assess the current situation (identify type of ransomware and damages) and start collecting forensic data. Decide if you will pay the ransom and/or if you will hire a negotiator that specializes in ransomware. Keep the attack confidential while you lay out your plan…continue to review the plan with your team…and then execute with vigor. You will then need to develop and implement a cybersecurity strategy moving forward and make this a consistent part of your overall business strategy.
2. How long does it take to recover from a ransomware attack?
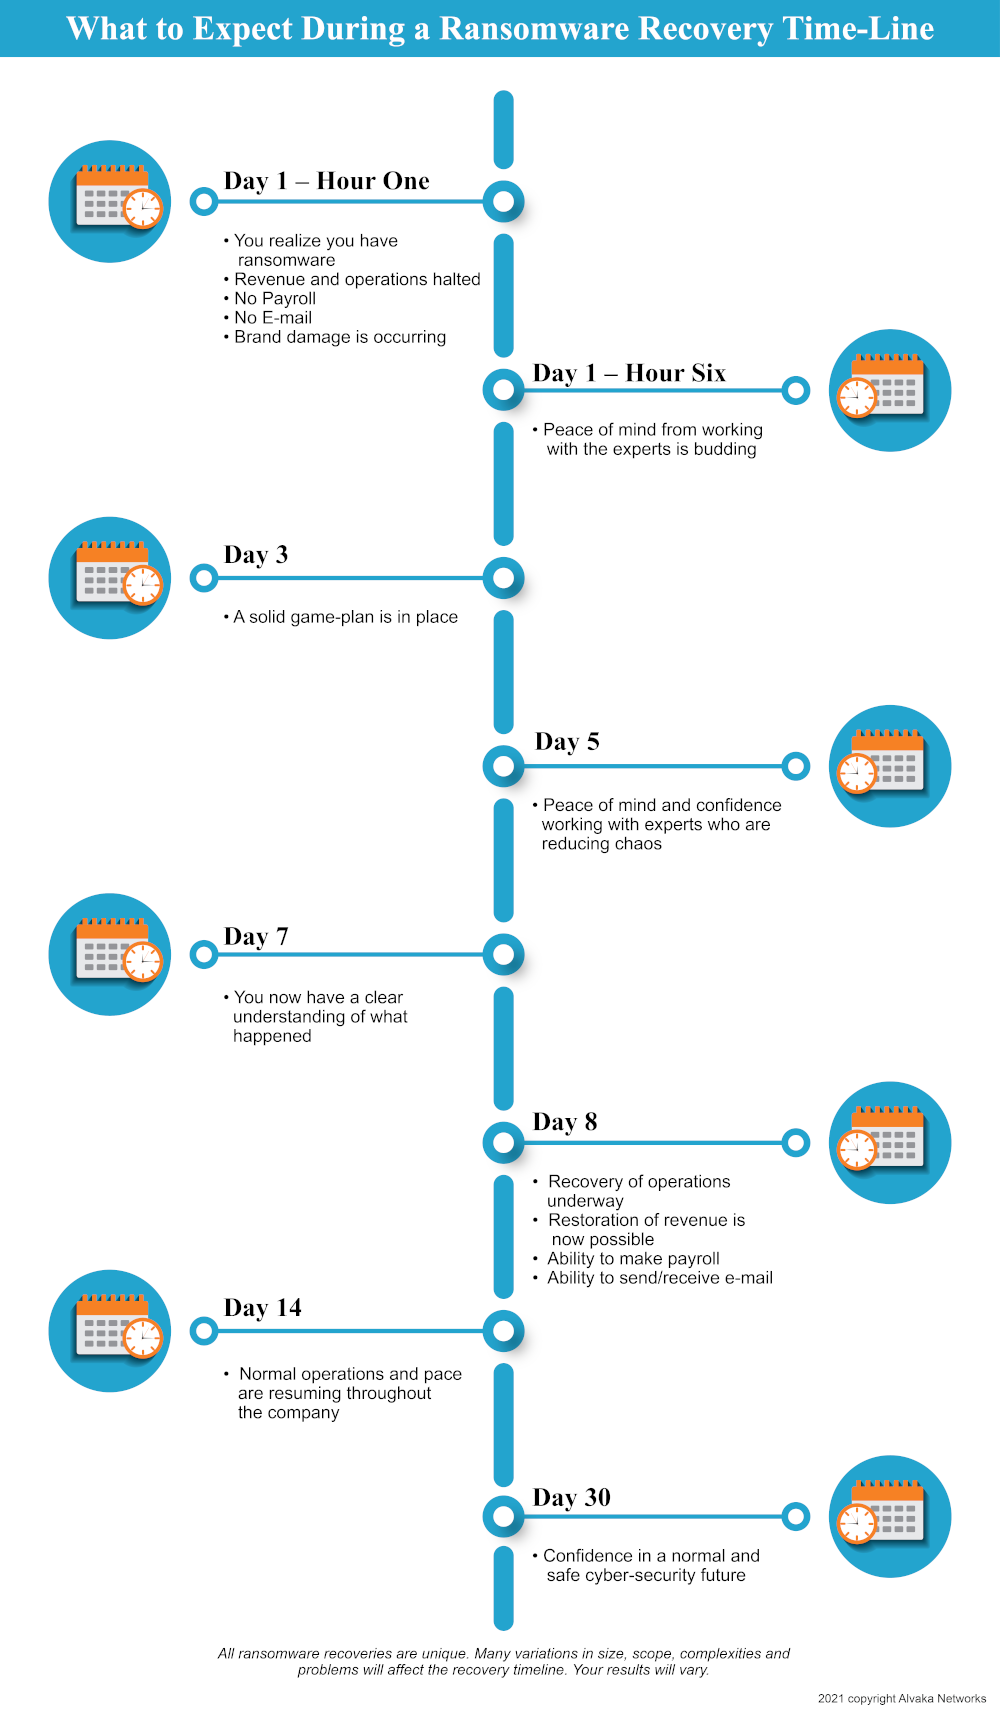
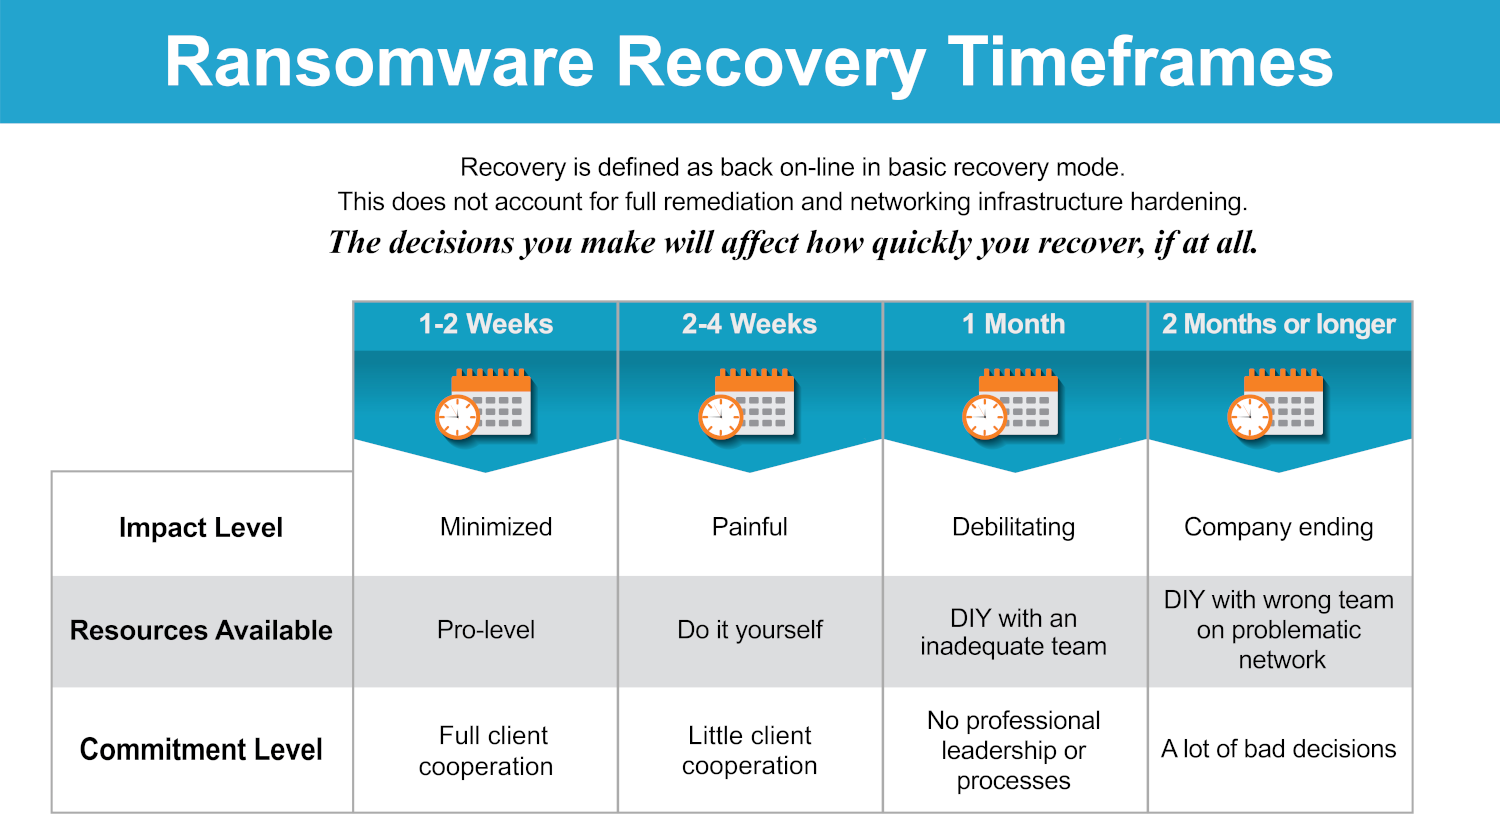
The time it takes to recover from a ransomware attack can vary widely. For most companies who are unprepared and unexperienced, recovery efforts will typically fall between the two to four week mark. However, recovery time can be cut in half (about one to two weeks) if you have a well-managed effort and experienced team.
Prolonged recovery efforts are a result of many factors, and often come at the expense of the company’s bottom line and reputation. In some cases, the company may never recover. It is therefore crucial to consider all of the variables that can impact the time it takes to recover from an attack. Below are five variables we find to have the most influence.
1. The most important is having a well-coordinated and experienced team of experts (includes ransomware recovery team, insurance company, incident response team, lawyers, ransomware negotiator, etc.) 2. Type of ransomware and the experience level of the attackers. 3. Size of your IT infrastructure. 4. Configuration of your It infrastructure before the attack. 5. The experience level, maturity, and size of your IT team.
3. How much will it cost to recover from a ransomware attack?
If your company has been hit with ransomware, you might be wondering how much the incident will cost you. There are many variables that will determine your costs, including company size, the complexity of your network and applications, and which ransomware you have been infected with. There are two cost categories to consider: Cost to Recover and Total Cost of Ransomware Recovery (TCRR).
The Cost to Recover includes the amount of cash you will need to pay out for recovery activities like incident response, decryption and system recovery, forensics, and the ransom amount paid (if any). The Total Cost of Ransomware Recovery (TCRR) will also include the lost revenue associated with the incident, due to downtime, brand reputation, etc. Your downtime will vary depending on the specifics of your attack.
We have created a Ransomware Recovery Cost Calculator that will help you determine your estimated TCRR.
skip render: ucaddon_creative_buttons
4. If I pay the ransomware demand, will I get my data back?
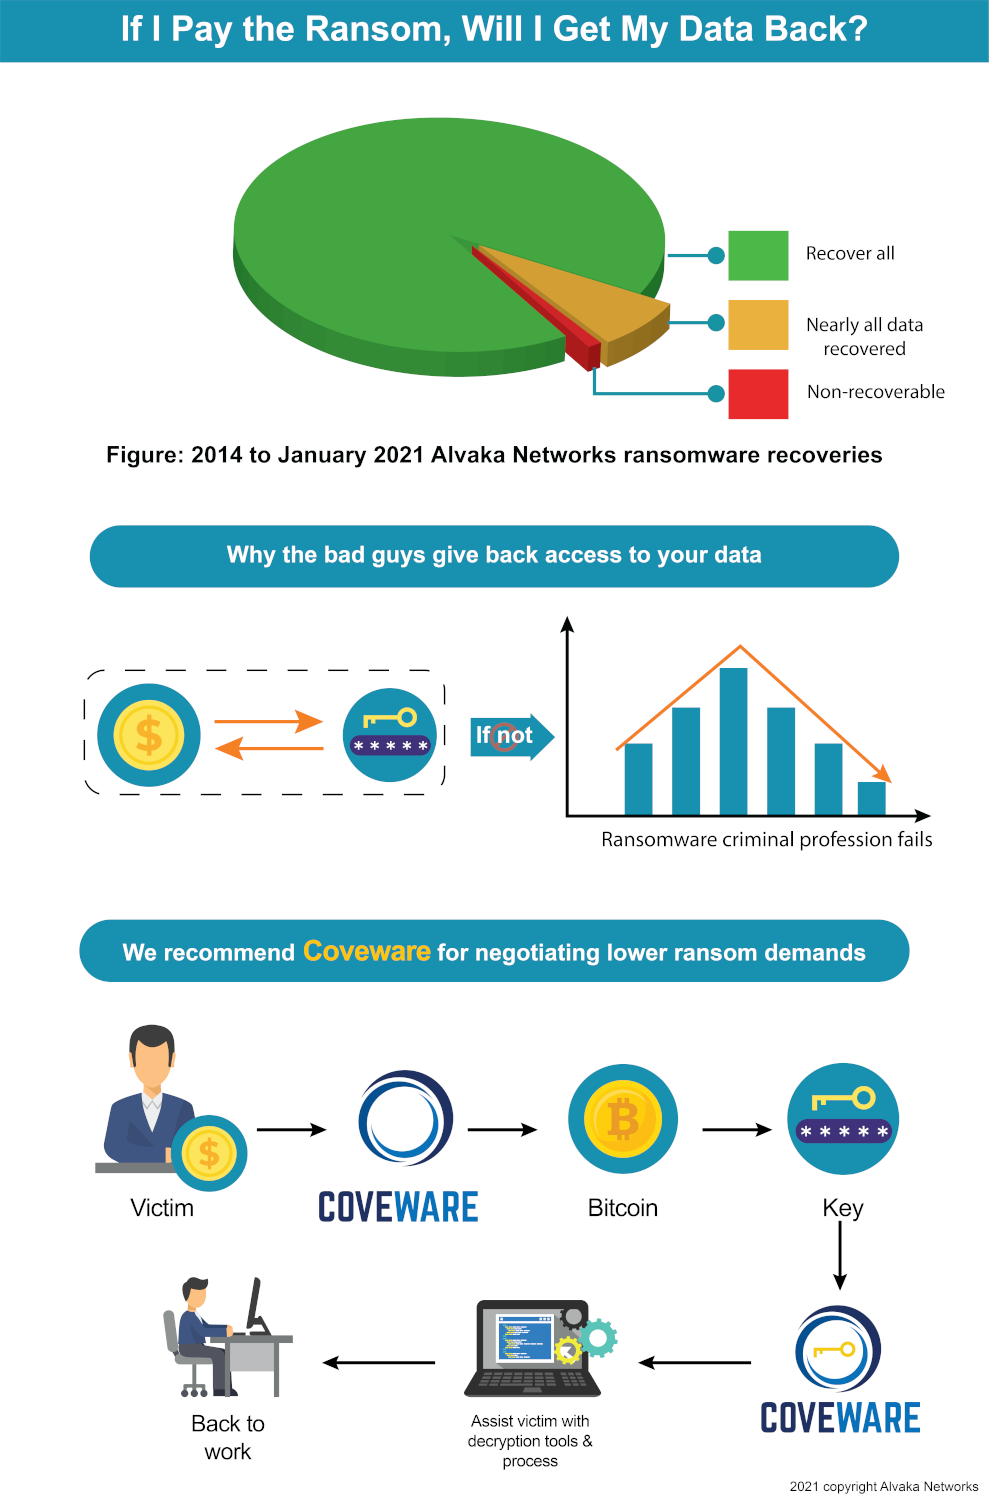
With any ransomware incident, you are dealing with criminals who will not hesitate to harm you further to receive payment out of you.
Additionally, the odds aren’t in your favor if your backups are outdated – like most ransomware victims. So, you are wondering, should I trust the word of these cybercriminals? No, you shouldn’t. However, these threat actors have a reputation they must maintain. If the cybercriminal industry is known for having individuals that don’t provide a decryption key when paid, well, then their leverage factor gets significantly reduced. No one would pay a ransom knowing that the most likely scenario will be they get scammed. These cybercriminals are making too much money, and they wouldn’t risk ruining that. Now, that doesn’t mean there have been zero instances where a cybercriminal didn’t provide a decryption key. Therefore, if you decide to pay a ransom, we recommend Coveware for the negotiation process.
5. How much is the average ransomware demand?
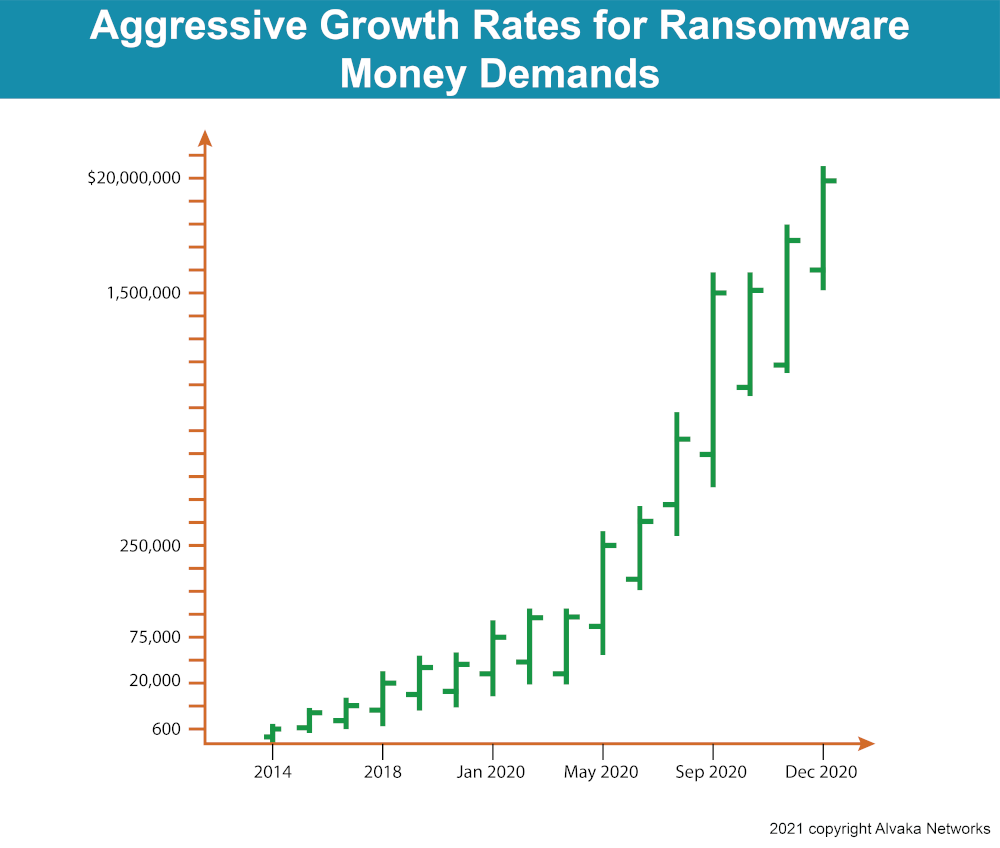
Each ransom attack can vary significantly, so it quite difficult to pinpoint the exact amount of a typically demanded in ransomware cases. However, history shows a clear trend – an increasing ransom amount. In the early years, a $200M per year company would only expect a ransom of a few hundred dollars.
By 2018, threat actors became more efficient and created in-depth plans, allowing them to price a ransom proportionally with a company’s size. In 2020, a typical ransom for a company producing $20M annually would receive a ransom amount of $50-100k. By the end of the year, ransoms were pushing themselves into the millions, and in November, we saw our first $20M ransom.
Overall, the ransom amount depends on many factors, like what tools the threat actors are using, number of servers, number of files, total storage, and more. Additionally, according to a report by Coveware, ransom payments are increasing (see Ransomware will likely get worse in 2021), and findings show that the typical ransom amount has risen 31% to $233,817, as of late 2020.
6. Who are the best ransomware recovery service companies?
Alvaka has been involved in many recovery efforts and have first-hand experience working with companies that offer specific services when it comes to recovering from ransomware. The ransomware recovery process is complex and will require building a response team specific to your ransomware incident in order to be successful in your efforts.
Ransomware recovery service companies fall into three primary categories:
Ransomware negotiation/decryption
Incident response/containment
Ransomware recovery/IT system rebuilding and recovery
It is unlikely you will find one ransomware recovery service company that offers the full stack of recovery services you need, so you will need to determine what you need and choose accordingly. Here are our recommendations for the Best Ransomware Recovery Services Companies.
7. Should I engage a lawyer after a cyber attack? Who are the best ransomware lawyers and cyber breach coaches?
Another crucial addition to your ransomware recovery response team should include a ransomware or cyber breach lawyer, usually specializing in ransomware, data exfiltration and phishing related business email compromise. They will be your trusted advisor throughout your ransomware and cyber breach recovery journey. A ransomware attack does not just cause a dire technical and business issue, but in many cases it can be a legal issue as well.
A ransomware and cyber breach lawyer will:
engage and manage all parties involved in the recovery process
provide important legal protections via attorney client privilege
ensure compliance with the law
help minimize and manage aftermath of a data compromise
Ransomware attacks are becoming increasingly common, and whether you are a small, medium, or large company, you are a target.
If you have been an unfortunate victim of a ransomware attack, you are likely overwhelmed and wondering what the next steps are. We have been involved in many recovery efforts and have outlined what our clients experience as the most common and important steps when recovering from a ransomware attack.
The process will be lengthy, expensive, and stressful but putting together a well-rounded recovery and response team will be invaluable. In the initial stages, engage a lawyer and find out what insurance covers. Have your response team assess the current situation (identify type of ransomware and damages) and start collecting forensic data. Decide if you will pay the ransom and/or if you will hire a negotiator that specializes in ransomware. Keep the attack confidential while you lay out your plan…continue to review the plan with your team…and then execute with vigor. You will then need to develop and implement a cybersecurity strategy moving forward and make this a consistent part of your overall business strategy.
The time it takes to recover from a ransomware attack can vary widely. For most companies who are unprepared and unexperienced, recovery efforts will typically fall between the two to four week mark. However, recovery time can be cut in half (about one to two weeks) if you have a well-managed effort and experienced team.
Prolonged recovery efforts are a result of many factors, and often come at the expense of the company’s bottom line and reputation. In some cases, the company may never recover. It is therefore crucial to consider all of the variables that can impact the time it takes to recover from an attack. Below are five variables we find to have the most influence.
1. The most important is having a well-coordinated and experienced team of experts (includes ransomware recovery team, insurance company, incident response team, lawyers, ransomware negotiator, etc.) 2. Type of ransomware and the experience level of the attackers. 3. Size of your IT infrastructure. 4. Configuration of your It infrastructure before the attack. 5. The experience level, maturity, and size of your IT team.
If your company has been hit with ransomware, you might be wondering how much the incident will cost you. There are many variables that will determine your costs, including company size, the complexity of your network and applications, and which ransomware you have been infected with. There are two cost categories to consider: Cost to Recover and Total Cost of Ransomware Recovery (TCRR).
The Cost to Recover includes the amount of cash you will need to pay out for recovery activities like incident response, decryption and system recovery, forensics, and the ransom amount paid (if any). The Total Cost of Ransomware Recovery (TCRR) will also include the lost revenue associated with the incident, due to downtime, brand reputation, etc. Your downtime will vary depending on the specifics of your attack.
We have created a Ransomware Recovery Cost Calculator that will help you determine your estimated TCRR.
skip render: ucaddon_creative_buttons
With any ransomware incident, you are dealing with criminals who will not hesitate to harm you further to receive payment out of you.
Additionally, the odds aren’t in your favor if your backups are outdated – like most ransomware victims. So, you are wondering, should I trust the word of these cybercriminals? No, you shouldn’t. However, these threat actors have a reputation they must maintain. If the cybercriminal industry is known for having individuals that don’t provide a decryption key when paid, well, then their leverage factor gets significantly reduced. No one would pay a ransom knowing that the most likely scenario will be they get scammed. These cybercriminals are making too much money, and they wouldn’t risk ruining that. Now, that doesn’t mean there have been zero instances where a cybercriminal didn’t provide a decryption key. Therefore, if you decide to pay a ransom, we recommend Coveware for the negotiation process.
Each ransom attack can vary significantly, so it quite difficult to pinpoint the exact amount of a typically demanded in ransomware cases. However, history shows a clear trend – an increasing ransom amount. In the early years, a $200M per year company would only expect a ransom of a few hundred dollars.
By 2018, threat actors became more efficient and created in-depth plans, allowing them to price a ransom proportionally with a company’s size. In 2020, a typical ransom for a company producing $20M annually would receive a ransom amount of $50-100k. By the end of the year, ransoms were pushing themselves into the millions, and in November, we saw our first $20M ransom.
Overall, the ransom amount depends on many factors, like what tools the threat actors are using, number of servers, number of files, total storage, and more. Additionally, according to a report by Coveware, ransom payments are increasing (see Ransomware will likely get worse in 2021), and findings show that the typical ransom amount has risen 31% to $233,817, as of late 2020.
Alvaka has been involved in many recovery efforts and have first-hand experience working with companies that offer specific services when it comes to recovering from ransomware. The ransomware recovery process is complex and will require building a response team specific to your ransomware incident in order to be successful in your efforts.
Ransomware recovery service companies fall into three primary categories:
Ransomware negotiation/decryption
Incident response/containment
Ransomware recovery/IT system rebuilding and recovery
It is unlikely you will find one ransomware recovery service company that offers the full stack of recovery services you need, so you will need to determine what you need and choose accordingly. Here are our recommendations for the Best Ransomware Recovery Services Companies.
Another crucial addition to your ransomware recovery response team should include a ransomware or cyber breach lawyer, usually specializing in ransomware, data exfiltration and phishing related business email compromise. They will be your trusted advisor throughout your ransomware and cyber breach recovery journey. A ransomware attack does not just cause a dire technical and business issue, but in many cases it can be a legal issue as well.
A ransomware and cyber breach lawyer will:
engage and manage all parties involved in the recovery process
provide important legal protections via attorney client privilege
ensure compliance with the law
help minimize and manage aftermath of a data compromise
Each year, more sophisticated and harder-to-detect ransomware variants are developed and deployed onto unsuspecting companies. Having access to valuable and reliable ransomware resources and information can make all the difference.
When you’ve become a victim of ransomware, the crucial first step to recovery is to identify which variant the threat actors used. From there, the experience and knowledge of a professional ransomware removal team can be very beneficial.
There are many free, easy, and reliable ways to identify which ransomware variant has infected you. Once identification of the ransomware variant is successful, the recovery process via the deployment of an effective plan can begin. The specifics of each incident and what they require will vary from case to case, but you can generally expect common essential steps in a recovery effort.
How do I prepare in advance to reduce the risk of ransomware and other cyber attacks?
As a network security provider, we have seen first-hand what the long and painful road to ransomware recovery can involve. The recovery process can take months and carry significant costs beyond insurance coverage and ransom demand. Fortunately, you can take steps to reduce your chances of becoming a victim.
Implement the below actions to reduce the risk of ransomware and other cyber attacks:
• Require multi-factor authentication
• Patch ALL systems frequently
• Manage or Remove Deprecated or End-Of-Life systems
• Update Firewalls and other firmware
• Enable strong spam (email) filters
• Implement user training and simulated attacks
• Filter network traffic
• Implement URL reputation services
• Limit access to data and other assets. Segment your network!
• Restrict remote systems access
• Use active scan antivirus/antimalware
• Remove all local admin rights and restrict non-IT staff rights
• If you can, BLOCK (and if not, Disable) Office macros
• Implement a backup system that covers all critical data and system states. Isolate backups from the network; institute insider protections; store offline image templates, license keys, source code and copies of executables
• Get breach insurance that covers ransomware
• Ensure your exception-based monitoring can immediately trigger alerts
• Create a Business Continuity Plan (BCP) for security events
Should I Buy Cyber Breach Insurance? And Why?
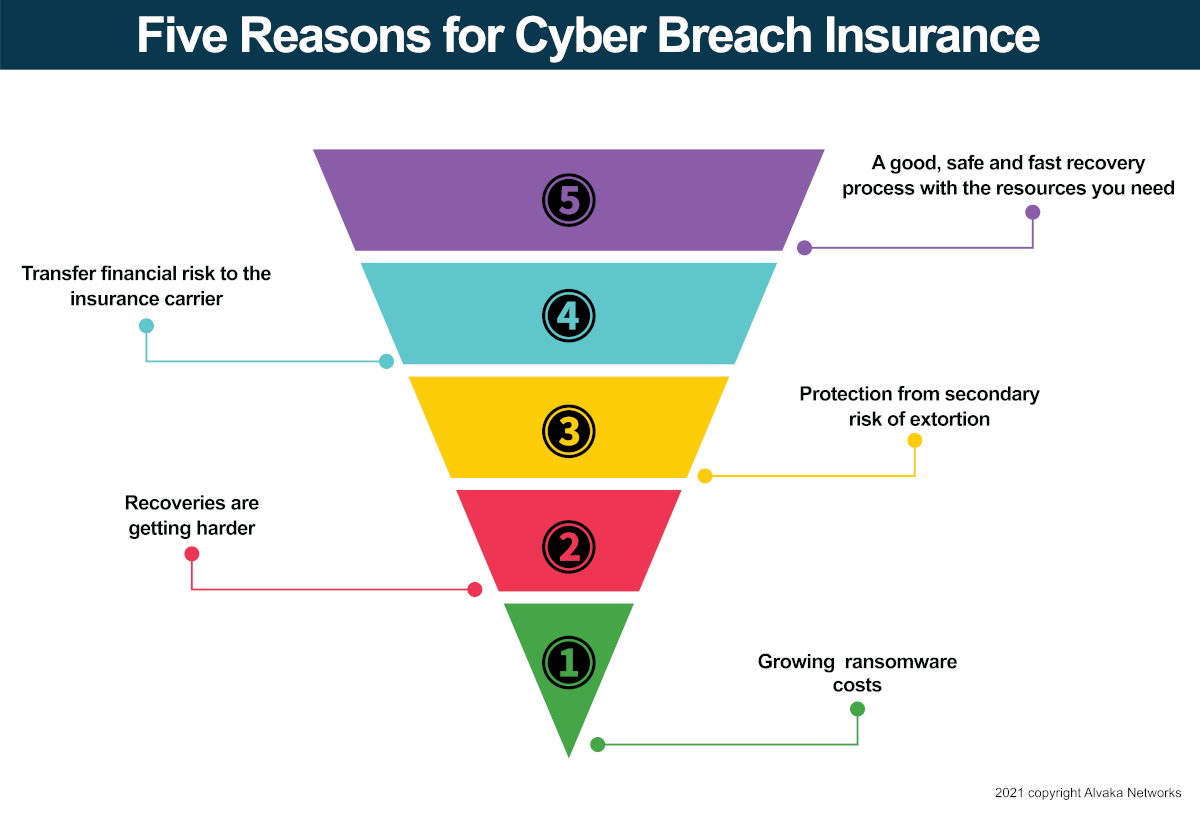
Cyber breach insurance has grown to be a valuable asset over the last few years due to constantly changing trends in cybersecurity and threat actor tactics. So, should you invest in cyber breach insurance in 2021? Yes, and we’ll list out the top 5 reasons why you should.
1. The trends are against you. Each year, threat actors become more efficient and smarter in proportionally pricing a ransom to your company’s size. In the early years, a typical ransom would have cost only a few hundred dollars, but now threat actors can accurately estimate your revenue and price accordingly.
2. Unfortunately, it is harder to recover from ransomware than before. In 2018, a nasty habit among threat actors developed – deletion of backups. Now, you can expect cybercriminals to learn everything about your network, attack with a plan, delete backups, and encrypt all your data.
3. Not only will they delete and encrypt files, but they will also attempt to extort you by threatening to sell your confidential information.
4. This one is obvious. The transfer of risk to the insurance carrier. Also, ensure your cyber breach insurance covers the ransom, forensic, ransom negotiation, legal representation, ransomware recovery, public relations, fines and breach notification, and business interruption.
5. Following a sound ransomware recovery process with adequate resources is key.
skip render: ucaddon_creative_buttons
How much cyber breach insurance do I need?
When it comes to cybersecurity threats and the potential losses, business decision makers might be wondering just how much cyber breach insurance coverage they need. A simple answer to this, given averages and trends, is that your coverage should range from at least $1,000,000 to $5,000,000. Additionally, you will want to make sure your total limit is around 10% to 20% of your annual revenue to cover business interruption losses.
A more analytical process to determine what your coverage should be is to estimate how much a cyber incident, like ransomware, is likely to cost you if your company were attacked. Getting hit with ransomware is certainly not the only reason you would need cyber breach coverage, however, we recommend using a ransomware breach as the best indicator for how much coverage you should buy due to the following…
Ransomware is the most prevalent cyber breach incident, with significant cost implications
Ransomware attacks commonly include an extortion demand, with bad actors threatening to release data that was exfiltrated from the victims’ network
Ransomware attack cost components include every expense category involved in a cyber breach event, including legal counsel, incident response, digital forensics, ransom negotiation, and more
To estimate your cost of a ransomware attack, you can use our Ransomware Recovery Cost Calculator below. The calculator calculates in real time and we encourage you to play with some differing values in some “what if” type situations.
skip render: ucaddon_creative_buttons
Each year, more sophisticated and harder-to-detect ransomware variants are developed and deployed onto unsuspecting companies. Having access to valuable and reliable ransomware resources and information can make all the difference.
When you’ve become a victim of ransomware, the crucial first step to recovery is to identify which variant the threat actors used. From there, the experience and knowledge of a professional ransomware removal team can be very beneficial.
There are many free, easy, and reliable ways to identify which ransomware variant has infected you. Once identification of the ransomware variant is successful, the recovery process via the deployment of an effective plan can begin. The specifics of each incident and what they require will vary from case to case, but you can generally expect common essential steps in a recovery effort.
As a network security provider, we have seen first-hand what the long and painful road to ransomware recovery can involve. The recovery process can take months and carry significant costs beyond insurance coverage and ransom demand. Fortunately, you can take steps to reduce your chances of becoming a victim.
Implement the below actions to reduce the risk of ransomware and other cyber attacks:
• Require multi-factor authentication
• Patch ALL systems frequently
• Manage or Remove Deprecated or End-Of-Life systems
• Update Firewalls and other firmware
• Enable strong spam (email) filters
• Implement user training and simulated attacks
• Filter network traffic
• Implement URL reputation services
• Limit access to data and other assets. Segment your network!
• Restrict remote systems access
• Use active scan antivirus/antimalware
• Remove all local admin rights and restrict non-IT staff rights
• If you can, BLOCK (and if not, Disable) Office macros
• Implement a backup system that covers all critical data and system states. Isolate backups from the network; institute insider protections; store offline image templates, license keys, source code and copies of executables
• Get breach insurance that covers ransomware
• Ensure your exception-based monitoring can immediately trigger alerts
• Create a Business Continuity Plan (BCP) for security events
Cyber breach insurance has grown to be a valuable asset over the last few years due to constantly changing trends in cybersecurity and threat actor tactics. So, should you invest in cyber breach insurance in 2021? Yes, and we’ll list out the top 5 reasons why you should.
1. The trends are against you. Each year, threat actors become more efficient and smarter in proportionally pricing a ransom to your company’s size. In the early years, a typical ransom would have cost only a few hundred dollars, but now threat actors can accurately estimate your revenue and price accordingly.
2. Unfortunately, it is harder to recover from ransomware than before. In 2018, a nasty habit among threat actors developed – deletion of backups. Now, you can expect cybercriminals to learn everything about your network, attack with a plan, delete backups, and encrypt all your data.
3. Not only will they delete and encrypt files, but they will also attempt to extort you by threatening to sell your confidential information.
4. This one is obvious. The transfer of risk to the insurance carrier. Also, ensure your cyber breach insurance covers the ransom, forensic, ransom negotiation, legal representation, ransomware recovery, public relations, fines and breach notification, and business interruption.
5. Following a sound ransomware recovery process with adequate resources is key.
skip render: ucaddon_creative_buttons
When it comes to cybersecurity threats and the potential losses, business decision makers might be wondering just how much cyber breach insurance coverage they need. A simple answer to this, given averages and trends, is that your coverage should range from at least $1,000,000 to $5,000,000. Additionally, you will want to make sure your total limit is around 10% to 20% of your annual revenue to cover business interruption losses.
A more analytical process to determine what your coverage should be is to estimate how much a cyber incident, like ransomware, is likely to cost you if your company were attacked. Getting hit with ransomware is certainly not the only reason you would need cyber breach coverage, however, we recommend using a ransomware breach as the best indicator for how much coverage you should buy due to the following…
Ransomware is the most prevalent cyber breach incident, with significant cost implications
Ransomware attacks commonly include an extortion demand, with bad actors threatening to release data that was exfiltrated from the victims’ network
Ransomware attack cost components include every expense category involved in a cyber breach event, including legal counsel, incident response, digital forensics, ransom negotiation, and more
To estimate your cost of a ransomware attack, you can use our Ransomware Recovery Cost Calculator below. The calculator calculates in real time and we encourage you to play with some differing values in some “what if” type situations.
Stop being a victim of Ransomware and take action today!
Maybe you think that you’re not in any danger and that you take all the necessary precautions. Maybe you believe that you’ve educated your employees enough on the risks of random downloads, clicking on unsecured links, and opening strange emails.
RobbinHood Ransomware Data Recovery Services
Being a victim of ransomware is draining to the performance, finances, and growth of a company. If you ever fall under the unfortunate circumstances of being a victim, immediately seek professional help to resolve the issue. At Alvaka, our team of professionals is equipped with the skill and resources to deal with all variants of ransomware: including RobbinHood. Time is of the essence when it comes to a potential or existing network compromise, and you can count on Alvaka to swiftly recover your business.
What Exactly Is RobbinHood Ransomware?
RobbinHood Ransomware is a variant of ransomware that is, like other common variants, “human-operated,” and “typically start with an RDP brute-force attack against an exposed asset” (Microsoft). An RDP brute-force attack is when a hacker uses an automated tool that tries numerous combinations of usernames and passwords to gain access into the target’s computer. Eventually, the cybercriminal gains access and then uses that account’s information to, “obtain privileged credentials, mostly local administrator accounts with shared or common passwords, and service accounts with domain admin privileges” (Microsoft). Once they have gathered up enough accounts, they leave behind local accounts in the Active Directory to easily gain access at another time.
What You Can Expect from Alvaka
Paying a ransom never guarantees a cybercriminal will give you access to the files they have encrypted. Additionally, paying gives the attacker an incentive to come back later. At Alvaka, we recommend you seek qualified assistance to handle the recovery of your network. Our staff is ready 24×7×365 to deliver quality assistance in any malicious IT event. We take the extra steps to ensure that your network is eradicated of any weaknesses that could lead to any future complications.
Alvaka RobbinHood Ransomware Recovery Services are designed to help companies recover from ransomware attacks and protect your systems from future attacks.
Is there a REvil decryption key available? YES Search the No More Ransomware Decryption Toolswebpage to find the decryptor for the ransomware you’ve been hit with.
REvil Ransomware Recovery Services
Business downtime resulting from a network breach can be devastating to a company’s productivity and revenue. Priority should be placed on swiftly bringing the business back up and running, or else it could face possible bankruptcy. With Alvaka, your priority to recover becomes ours. Our determined and talented staff is ready 24×7×365 to defend and combat numerous varieties of ransomware attacks, including REvil.
What is REvil Ransomware?
REvil, also called Sodinokibi, is a variant of ransomware that exploits vulnerabilities in network devices in Pulse VPN. Cybercriminals use the vulnerabilities to obtain administrative credentials to access networks and steal the documents of customers, and any other possible data they can retrieve. The stolen data then gets uploaded to a site called “Happy Blog” and “the ransomware gang uses the site to post samples of the stolen data and then threaten to release the actual files” (BleepingComputer). REvil operators use techniques that are similar to other variants of ransomware. Tools such as Mimikatz and PsExec are used to laterally spread within a network and perform reconnaissance to check which servers and workstations are exposed.
What You Can Expect from Alvaka
You must reach out for professional help immediately after being attacked by ransomware. The faster you react, the better your chances of being able to recover most, if not all, of your data. Surrendering your assets via payment of a ransom only gives an incentive for cybercriminals to attack again. You can expect our staff at Alvaka to work effectively to purge your network, servers, and workstations of all traces of ransomware. We also scan for possible weaknesses to prevent future ransomware events from occurring. If your business has been hit by ransomware, do not hesitate to give us a call.https://www.youtube.com/watch?v=AK8lfAzQmkg&source_ve_path=OTY3MTQ&embeds_referring_euri=https%3A%2F%2Fwww.alvaka.net%2FAlvaka REvil Ransomware Recovery Services are designed to help companies recover from ransomware attacks and protect your systems from future attacks.
Stop being a victim of Ransomware and take action today! Maybe you think that you’re not in any danger and that you take all the necessary precautions. Maybe you believe that you’ve educated your employees enough on the risks of random downloads, clicking on unsecured links, and opening strange emails.
PonyFinal Ransomware Recovery Services
Being an unfortunate victim of ransomware can have devastating effects on the financial condition, growth, and performance of a company. One should always seek immediate professional help if a ransomware situation were to arise. Fortunately, Alvaka offers an exceptional team of professionals equipped with the resources and skills to deal with many types of ransomware incidents – including PonyFinal. Time is a crucial component of our work method, and you can count on us to quickly recover your business.
What is PonyFinal Ransomware?
PonyFinal Ransomware is a type of ransomware that is Java-based. Usually, it is considered a novelty but the campaign methods used by cybercriminals are very common and destructive. In order for cybercriminals to “establish persistence, they [use] PowerShell commands to launch the system tool mshta.exe and set up a reverse shell based on the common PowerShell attack framework.” Additionally, they use other cyber tools, such as Splashtop, to keep remote desktop connections open to systems with administrative access privileges.
What to Expect from Your PonyFinal Ransomware Removal Company
At Alvaka, you can expect us to provide your company with a highly qualified staff that is ready to respond to your needs 24×7×365. Paying a ransomware never guarantees that you will get your data back, but it will certainly give cybercriminals an incentive to strike again. We suggest your first step to battling ransomware is contacting a professional team, and if you find yourself a victim of ransomware, do not hesitate to give us a call.https://www.youtube.com/watch?v=AK8lfAzQmkg&source_ve_path=OTY3MTQ&embeds_referring_euri=https%3A%2F%2Fwww.alvaka.net%2FAlvaka’s PonyFinal Ransomware Recovery Services are designed to help companies recover from ransomware attacks and protect systems from future attacks.
Stop being a victim of Ransomware and take action today!
Maybe you think that you’re not in any danger and that you take all the necessary precautions. Maybe you believe that you’ve educated your employees enough on the risks of random downloads, clicking on unsecured links, and opening strange emails.
NetWalker Ransomware Prevention Services
During a ransomware network breach, your first step should be to seek professional assistance. It is important to note that business downtime will produce disastrous results when not dealt with immediately. With Alvaka, our highly skilled and resourceful team is ready to combat and defend against potential or existing ransomware events. Our expertise in numerous types of ransomware, including NetWalker, allows us to be properly equipped to recover your business.
What Is NetWalker Ransomware?
NetWalker ransomware is a new campaign started by cybercriminals to infect hospitals and other healthcare networks by utilizing emails that appear to contain information about coronavirus (Covid-19). The email contains a .vbs attachment that “contains an embedded NetWalker Ransomware executable and obfuscated code to extract and launch it on the computer” (BleepingComputer). Alternatively, they also use misconfigured IIS-based applications to gather credentials. Although the NetWalker campaign is new, these strategies deployed by cybercriminals are already known.
Victims will know when they have been infiltrated as notice will be left behind for them to see. The notice will include information and instructions on how to obtain cryptocurrency in order to pay the requested ransom.
What You Can Expect from Alvaka
If you ever find yourself a victim of ransomware, we suggest you immediately seek professional help. Paying the ransom should be your last option, and it is important to remember that paying will not guarantee full, or any, data recovery. With Alvaka, you can expect our highly-skilled, determined, and responsive team to work diligently to recover your computer environments, stations and servers.
Alvaka’s NetWalker Ransomware Recovery Services are designed to help companies recover from ransomware attacks and protect their systems from future attacks.
Stop being a victim of Ransomware and take action today! Maybe you think that you’re not in any danger and that you take all the necessary precautions. Maybe you believe that you’ve educated your employees enough on the risks of random downloads, clicking on unsecured links, and opening strange emails.
AKO Ransomware Data Recovery Services
With downtime severely impacting company performance in all sectors, you can depend on Alvaka to make your data recovery our top priority. Our well-equipped team of professionals have helped countless businesses recover from ransomware: including AKO attacks.
What is AKO?
AKO is a variant type of ransomware that can be separated into two categories. The difference between the two lies within the way that the victims are meant to make contact with the hacker and/or pay a ransom. When you’re the victim of an AKO attack of any nature, a ransom note is created as a text file that will show like this: ako-readme.txt. In one version, you will be directed to pay the ransom via a Tor site. In the other, there will be instructions to send an email to the cybercriminals. Both types of AKO will generate an id.key, dropping it into your folders that have encrypted files and renaming them all.
AKO Ransomware Recovery Consulting Services by Alvaka
With Alvaka, you’ll have a highly qualified team ready to immediately begin recovering your information. We also investigate the cause of your attack and implement the proper techniques so you don’t become a victim again. We recommend that you do not pay the ransom since it is not going to guarantee that the criminals will give you back your files.https://www.youtube.com/watch?v=AK8lfAzQmkgAlvaka Cybersecurity Solutions are designed to protect your company’s systems from Ransomware and help you recovery when necessary.
Stop being a victim of Ransomware and take action today!
Maybe you think that you’re not in any danger and that you take all the necessary precautions. Maybe you believe that you’ve educated your employees enough on the risks of random downloads, clicking on unsecured links, and opening strange emails.
SamSam Ransomware Recovery Services
When it comes to cyberattacks, ransomware is one of the most vicious hacks that a criminal has in their arsenal. The cruel notion of taking someone’s data and personal belongings and holding them to ransom over a digital system is one that should strike fear into any innocent technology user.
Here, we’ll let you know about a kind of ransomware, named SamSam ransomware, that many cybercriminals utilize, and how Alvaka will be able to help you should you ever come into that kind of trouble in the future.
So, What Actually Is SamSam Ransomware?
SamSam is different from typical ransomware as it stays inside a system and spies for a while without being spotted or detected. During that time, the ransomware is mapping out your entire network architecture so that it can encrypt every single possible file. The malicious software will slowly make its way through a vulnerable system using brute-force tactics and later make it next to impossible for the victim to access any of their own private info and data. The cybercriminals will then want a ransom – usually money. These criminals are known for hacking large businesses that will provide them with lots of money, but they also target smaller businesses, too.
Victims will know when they have been infiltrated as notice will be left behind for them to see. The notice will include information and instructions on how to obtain cryptocurrency in order to pay the requested ransom.
How Does SamSam Ransomware Impact Victims?
If the victim is not protected enough, the cybercriminals will be able to infiltrate a lot more, meaning they are even more likely to be successful in their theft. A user’s entire funds can be drained if they are not careful. There have been many, many cases of SamSam ransomware attacks in recent years, and millions of dollars have been stolen. The USA experienced this badly in 2018 as the first quarter, nearly a dozen healthcare organizations were targeted. The city of Atlanta also lost over seven million dollars, according to reports.
How Long Does It Take to Recover from a SamSam Ransomware Attack?
While being attacked in this manner is far from ideal, the process is usually a quick one due to the way in which the cybercriminals operate. Your system can be back up and running fairly quickly, but your other aspects depend on how heavy you are hit, of course.
What Can We Do to Help?
We will work hard for you. We will protect you from losing money, information, and time. We will watch over your systems and detect any threats. We will educate you and your team on how to take the right steps going forward.
We have a high-trained and experienced team ready to get you out of any mess you may have found yourself in. We will be on the pulse with as much support as we can possibly provide. We feel it is our duty to not only return to you what is rightfully yours but also take the appropriate steps to stop anything similar from happening ever again.
How Can Further Attacks Be Prevented?
The best way is to get in touch with a firm like Alvaka and let us work together with you. As mentioned before, we have a trained and experienced group, so we know how to deal with such attacks. Purchasing the appropriate defense software is also key in stopping hackers from infiltrating your system(s) going forward.
Alvaka’s SamSam Ransomware Recovery Services are designed to help companies recover from ransomware attacks and protect your systems from future attacks.